Home > Software > libObfuscate Cryptography
libObfuscate  LGPLv3 Software
Modern 256bit Cryptography & Scrambling
ISO C / Open-source / System Independent

Architecture

Cipher selection
How to Link to your C project
go to \libObfuscateRedist\
add libObfuscateDef\*.h to your source
add libObfuscateDef.h to your source
add libObfuscate.h to your source
add #include "libObfuscate.h" to your files
link using libObfuscate.lib
add libObfuscate.dll (no dependencies) to your release
add full licensing license.txt to your release
Manual / HW Seed - Based on AES
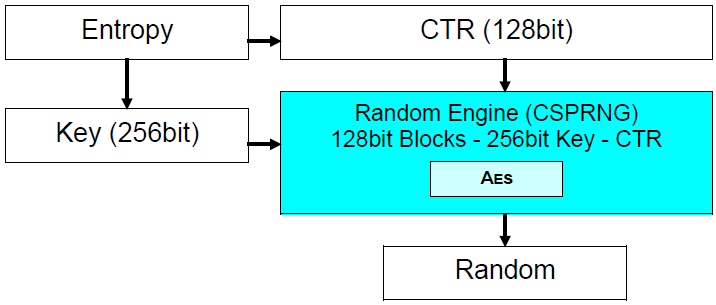
CSPRNG Architecture
// Manual Seed using Password + Nonce
// CSPRNG { Seed } = hash ( password + nonce )
// PARAM: hash + password[32] + nonce
typedef enum {
SHA512_HASH=0,
GROSTL512_HASH,
KECCAK512_HASH,
SKEIN512_HASH
} ENUM_HASH;
CSPRNG_set_seed (
CSPRNG_DATA &csprng,
ENUM_HASH hash,
BYTE *password,
DWORD nonce );
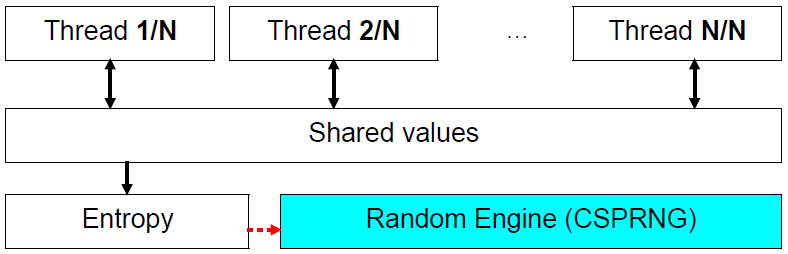
HW AutoSeed
// HW AutoSeed using RaceCondition
// CSPRNG { Seed } = HW Generated Entropy
// PARAM: progressCallback + progressDescriptor
// ( NULL + NULL ⇒ show no progress )
CSPRNG_autoseed (
CSPRNG_DATA *csprng,
perc_callback_t progressCallback,
void *progressDescriptor );
// Get Functions
BYTE randomByteValue =
CSPRNG_get_byte ( &csprng );
WORD randomWordValue =
CSPRNG_get_word ( &csprng );
DWORD randomDwordValue =
CSPRNG_get_dword ( &csprng );
// Array Functions
// buffer[length] = permutation { 0..length }
// PARAM: length < 0xFF + buffer[length]
CSPRNG_array_init (
CSPRNG_DATA *csprng,
DWORD length,
BYTE *buffer );
// buffer[length] = random bytes
// PARAM: length + buffer[length]
// PARAM: progressCallback + progressDescriptor
// ( NULL + NULL ⇒ show no progress )
// PARAM: stopCallback + stopDescriptor
// ( NULL + NULL ⇒ no stop test )
typedef enum {
OBFUNC_OK=0,
OBFUNC_OUTOFMEM,
OBFUNC_INVALID,
OBFUNC_STOP
} OBFUNC_RETV;
OBFUNC_RETV CSPRNG_randomize (
CSPRNG_DATA *csprng,
const DWORD length,
BYTE *buffer,
perc_callback_t progressCallback,
void *progressDescriptor,
test_callback_t stopCallback,
void *stopDescriptor );
Hashing
512bit Functions
SHA2 & SHA3 Process

512bit Hashing
// SHA2 Hashing Functions
// Original Submission Source
Sha512_init (
SHA512_DATA *sha );
Sha512_data (
SHA512_DATA *sha,
const void *buffer,
DWORD length );
Sha512_finalize (
SHA512_DATA *sha,
BYTE *hash );
// hash[64] = Sha512 ( buffer1[]..bufferN[] )
// PARAM: length1 + buffer1[length1]
// ...
// PARAM: lengthN + bufferN[lengthN]
Sha512_init ( &sha );
Sha512_data ( &sha, buffer1, length1 );
...
Sha512_data ( &sha, bufferN, lengthN );
Sha512_finalize ( &sha, hash );
// Grostl Hashing Functions
// Original Submission Source
Grostl512_init (
GROSTL512_DATA *grostl );
Grostl512_data (
GROSTL512_DATA *grostl,
const void *buffer,
DWORD length );
Grostl512_finalize (
GROSTL512_DATA *grostl,
BYTE *hash );
// hash[64] = Grostl512 ( buffer1[]..bufferN[] )
// PARAM: length1 + buffer1[length1]
// ...
// PARAM: lengthN + bufferN[lengthN]
Grostl512_init ( &grostl );
Grostl512_data ( &grostl, buffer1, length1 );
...
Grostl512_data ( &grostl, bufferN, lengthN );
Grostl512_finalize ( &grostl, hash );
// Skein Hashing Functions
// Original Submission Source
Skein512_init (
SKEIN512_DATA *skein );
Skein512_data (
SKEIN512_DATA *skein,
const void *buffer,
DWORD length );
Skein512_finalize (
SKEIN512_DATA *skein,
BYTE *hash );
// hash[64] = Skein512 ( buffer1[]..bufferN[] )
// PARAM: length1 + buffer1[length1]
// ...
// PARAM: lengthN + bufferN[lengthN]
Skein512_init ( &skein );
Skein512_data ( &skein, buffer1, length1 );
...
Skein512_data ( &skein, bufferN, lengthN );
Skein512_finalize ( &skein, hash );
// SHA3 (Keccak) Hashing Functions
// Original Submission Source
Keccak512_init (
KECCAK512_DATA *keccak );
Keccak512_data (
KECCAK512_DATA *keccak,
const void *buffer,
DWORD length );
Keccak512_finalize (
KECCAK512_DATA *keccak,
BYTE *hash );
// hash[64] = Keccak512 ( buffer1[]..bufferN[] )
// PARAM: length1 + buffer1[length1]
// ...
// PARAM: lengthN + bufferN[lengthN]
Keccak512_init ( &keccak );
Keccak512_data ( &keccak, buffer1, length1 );
...
Keccak512_data ( &keccak, bufferN, lengthN );
Keccak512_finalize ( &keccak, hash );
Cryptography
256bit key - 128bit block - ECB Ciphers
AES & NESSIE & CRYPTREC Process

256bit Cryptography
// AES (Rijndael) ECB Cipher Functions
// Original Submission Source
int Rijndael_set_key_encrypt (
DWORD *rijndaelKey,
const BYTE *key,
const int keyBits );
int Rijndael_set_key_decrypt (
DWORD *rijndaelKey,
const BYTE *key,
const int keyBits );
Rijndael_encrypt (
const DWORD *rijndaelKey,
const int numRounds,
const BYTE *plainText,
BYTE *cipherText );
Rijndael_decrypt (
const DWORD *rijndaelKey,
const int numRounds,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = AES ( plainText[16] )
// PARAM: password[32]
memset (
&rijndael, 0,
sizeof ( RIJNDAEL_STATIC_DATA ) );
rijndael.nrounds =
Rijndael_set_key_encrypt (
rijndael.key, password, 256 );
Rijndael_encrypt (
rijndael.key, rijndael.nrounds,
plainText, cipherText );
// plainText[16] = AES⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&rijndael, 0,
sizeof ( RIJNDAEL_STATIC_DATA ) );
rijndael.nrounds =
Rijndael_set_key_decrypt (
rijndael.key, password, 256 );
Rijndael_decrypt (
rijndael.key, rijndael.nrounds,
cipherText, plainText );
// Anubis ECB Cipher Functions
// Original Submission Source
Anubis_set_key (
ANUBIS_DATA *anubis,
const BYTE *key );
Anubis_encrypt (
const ANUBIS_DATA *anubis,
const BYTE *plainText,
BYTE *cipherText );
Anubis_decrypt (
const ANUBIS_DATA *anubis,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = Anubis ( plainText[16] )
// PARAM: password[32]
memset (
&anubis, 0,
sizeof ( ANUBIS_STATIC_DATA ) );
Anubis_set_key (
&anubis.key, password );
Anubis_encrypt (
&anubis.key, plainText, cipherText );
// plainText[16] = Anubis⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&anubis, 0,
sizeof ( ANUBIS_STATIC_DATA ) );
Anubis_set_key (
&anubis.key, password );
Anubis_decrypt (
&anubis.key, cipherText, plainText );
// Camellia ECB Cipher Functions
// Original Submission Source
Camellia_set_key (
BYTE *camelliaKey,
const int keyBits,
const BYTE *key );
Camellia_encrypt (
const BYTE *camelliaKey,
const int keyBits,
const BYTE *plainText,
BYTE *cipherText );
Camellia_decrypt (
const BYTE *camelliaKey,
const int keyBits,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = Camellia ( plainText[16] )
// PARAM: password[32]
memset (
&camellia, 0,
sizeof ( CAMELLIA_STATIC_DATA ) );
Camellia_set_key (
camellia.key, 256, password );
Camellia_encrypt (
camellia.key, 256,
plainText, cipherText );
// plainText[16] = Camellia⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&camellia, 0,
sizeof ( CAMELLIA_STATIC_DATA ) );
Camellia_set_key (
camellia.key, 256, password );
Camellia_decrypt (
camellia.key, 256,
cipherText, plainText );
// Cast256 ECB Cipher Functions
// Original Submission Source
Cast256_set_key (
DWORD *cast256Key,
const DWORD *key,
const DWORD keyBits );
Cast256_encrypt (
const DWORD *cast256Key,
const DWORD *plainText,
DWORD *cipherText );
Cast256_decrypt (
const DWORD *cast256Key,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = Cast256 ( plainText[16] )
// PARAM: password[32]
memset (
&cast256, 0,
sizeof ( CAST256_STATIC_DATA ) );
Cast256_set_key (
cast256.key, password, 256 );
Cast256_encrypt (
cast256.key, plainText, cipherText );
// plainText[16] = Cast256⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&cast256, 0,
sizeof ( CAST256_STATIC_DATA ) );
Cast256_set_key (
cast256.key, password, 256 );
Cast256_decrypt (
cast256.key, cipherText, plainText );
// Clefia ECB Cipher Functions
// Original Submission Source
Clefia_set_key (
CLEFIA_DATA *clefia,
const BYTE *key,
const int keyBits );
Clefia_encrypt (
const CLEFIA_DATA *clefia,
const BYTE *plainText,
BYTE *cipherText );
Clefia_decrypt (
const CLEFIA_DATA *clefia,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = Clefia ( plainText[16] )
// PARAM: password[32]
memset (
&clefia, 0,
sizeof ( CLEFIA_STATIC_DATA ) );
Clefia_set_key (
&clefia.key, password, 256 );
Clefia_encrypt (
&clefia.key, plainText, cipherText );
// plainText[16] = Clefia⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&clefia, 0,
sizeof ( CLEFIA_STATIC_DATA ) );
Clefia_set_key (
&clefia.key, password, 256 );
Clefia_decrypt (
&clefia.key, cipherText, plainText );
// FROG ECB Cipher Functions
// Original Submission Source
Frog_set_key (
FROG_DATA *frog,
const DWORD *key,
const DWORD keyBits );
Frog_encrypt (
const FROG_DATA *frog,
const DWORD plainText[4],
DWORD cipherText[4] );
Frog_decrypt (
const FROG_DATA *frog,
const DWORD cipherText[4],
DWORD plainText[4] );
// cipherText[16] = FROG ( plainText[16] )
// PARAM: password[32]
memset (
&frog, 0,
sizeof ( FROG_STATIC_DATA ) );
Frog_set_key (
&frog.key, password, 256 );
Frog_encrypt (
&frog.key, plainText, cipherText );
// plainText[16] = FROG⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&frog, 0,
sizeof ( FROG_STATIC_DATA ) );
Frog_set_key (
&frog.key, password, 256 );
Frog_decrypt (
&frog.key, cipherText, plainText );
// Hierocrypt3 ECB Cipher Functions
// Original Submission Source
Hierocrypt3_set_key (
HIEROCRYPT3_DATA *hierocrypt3,
const BYTE *key );
Hierocrypt3_encrypt (
const HIEROCRYPT3_DATA *hierocrypt3,
const BYTE *plainText,
BYTE *cipherText );
Hierocrypt3_decrypt (
const HIEROCRYPT3_DATA *hierocrypt3,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = Hierocrypt3 ( plainText[16] )
// PARAM: password[32]
memset (
&hierocrypt3, 0,
sizeof ( HIEROCRYPT3_STATIC_DATA ) );
Hierocrypt3_set_key (
&hierocrypt3.key, password );
Hierocrypt3_encrypt (
&hierocrypt3.key, plainText, cipherText );
// plainText[16] = Hierocrypt3⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&hierocrypt3, 0,
sizeof ( HIEROCRYPT3_STATIC_DATA ) );
Hierocrypt3_set_key (
&hierocrypt3.key, password );
Hierocrypt3_decrypt (
&hierocrypt3.key, cipherText, plainText );
// IdeaNXT ECB Cipher Functions
// Original Submission Source
Ideanxt128_set_key (
nxt128_ctx *ideanxt,
const BYTE *key,
const WORD keyBits );
Ideanxt128_encrypt (
const nxt128_ctx *ideanxt,
const BYTE *plainText,
BYTE *cipherText );
Ideanxt128_decrypt (
const nxt128_ctx *ideanxt,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = IdeaNXT ( plainText[16] )
// PARAM: password[32]
memset (
&ideanxt, 0,
sizeof ( IDEANXT128_STATIC_DATA ) );
Ideanxt128_set_key (
&ideanxt.key, password, 256 );
Ideanxt128_encrypt (
&ideanxt.key, plainText, cipherText );
// plainText[16] = IdeaNXT⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&ideanxt, 0,
sizeof ( IDEANXT128_STATIC_DATA ) );
Ideanxt128_set_key (
&ideanxt.key, password, 256 );
Ideanxt128_decrypt (
&ideanxt.key, cipherText, plainText );
// MARS ECB Cipher Functions
// Original Submission Source
Mars_set_key (
DWORD *marsKey,
DWORD *vk,
const DWORD *key,
const DWORD keyBits );
Mars_encrypt (
const DWORD *marsKey,
const DWORD *plainText,
DWORD *cipherText );
Mars_decrypt (
const DWORD *marsKey,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = MARS ( plainText[16] )
// PARAM: password[32]
memset (
&mars, 0,
sizeof ( MARS_STATIC_DATA ) );
mars.vk[0] = 0x09d0c479;
mars.vk[1] = 0x28c8ffe0;
mars.vk[2] = 0x84aa6c39;
mars.vk[3] = 0x9dad7287;
mars.vk[4] = 0x7dff9be3;
mars.vk[5] = 0xd4268361;
mars.vk[6] = 0xc96da1d4;
Mars_set_key (
mars.key, mars.vk, password, 256 );
Mars_encrypt (
mars.key, plainText, cipherText );
// plainText[16] = MARS⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&mars, 0,
sizeof ( MARS_STATIC_DATA ) );
mars.vk[0] = 0x09d0c479;
mars.vk[1] = 0x28c8ffe0;
mars.vk[2] = 0x84aa6c39;
mars.vk[3] = 0x9dad7287;
mars.vk[4] = 0x7dff9be3;
mars.vk[5] = 0xd4268361;
mars.vk[6] = 0xc96da1d4;
Mars_set_key (
mars.key, mars.vk, password, 256 );
Mars_decrypt (
mars.key, cipherText, plainText );
// RC6 ECB Cipher Functions
// Original Submission Source
Rc6_set_key (
DWORD *rc6Key,
const DWORD *key,
const DWORD keyBits );
Rc6_encrypt (
const DWORD *rc6Key,
const DWORD *plainText,
DWORD *cipherText );
Rc6_decrypt (
const DWORD *rc6Key,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = RC6 ( plainText[16] )
// PARAM: password[32]
memset (
&rc6, 0,
sizeof ( RC6_STATIC_DATA ) );
Rc6_set_key (
rc6.key, password, 256 );
Rc6_encrypt (
rc6.key, plainText, cipherText );
// plainText[16] = RC6⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&rc6, 0,
sizeof ( RC6_STATIC_DATA ) );
Rc6_set_key (
rc6.key, password, 256 );
Rc6_decrypt (
rc6.key, cipherText, plainText );
// Safer+ ECB Cipher Functions
// Original Submission Source
Saferp_set_key (
SAFERP_DATA *saferp,
const DWORD *key,
const DWORD keyBits );
Saferp_encrypt (
const SAFERP_DATA *saferp,
const DWORD *plainText,
DWORD *cipherText );
Saferp_decrypt (
const SAFERP_DATA *saferp,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = Safer+ ( plainText[16] )
// PARAM: password[32]
memset (
&saferp, 0,
sizeof ( SAFERP_STATIC_DATA ) );
Saferp_set_key (
&saferp.key, password, 256 );
Saferp_encrypt (
&saferp.key, plainText, cipherText );
// plainText[16] = Safer+⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&saferp, 0,
sizeof ( SAFERP_STATIC_DATA ) );
Saferp_set_key (
&saferp.key, password, 256 );
Saferp_decrypt (
&saferp.key, cipherText, plainText );
// SC2000 ECB Cipher Functions
// Original Submission Source
Sc2000_set_key (
DWORD *sc2000Key,
const DWORD *key );
Sc2000_encrypt (
const DWORD *sc2000Key,
const DWORD *plainText,
DWORD *cipherText );
Sc2000_decrypt (
const DWORD *sc2000Key,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = SC2000 ( plainText[16] )
// PARAM: password[32]
memset (
&sc2000, 0,
sizeof ( SC2000_STATIC_DATA ) );
Sc2000_set_key (
sc2000.key, password );
Sc2000_encrypt (
sc2000.key, plainText, cipherText );
// plainText[16] = SC2000⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&sc2000, 0,
sizeof ( SC2000_STATIC_DATA ) );
Sc2000_set_key (
sc2000.key, password );
Sc2000_decrypt (
sc2000.key, cipherText, plainText );
// Serpent ECB Cipher Functions
// Original Submission Source
Serpent_set_key (
DWORD *serpentKey,
const DWORD *key,
const DWORD keyBits );
Serpent_encrypt (
const DWORD *serpentKey,
const DWORD *plainText,
DWORD *cipherText );
Serpent_decrypt (
const DWORD *serpentKey,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = Serpent ( plainText[16] )
// PARAM: password[32]
memset (
&serpent, 0,
sizeof ( SERPENT_STATIC_DATA ) );
Serpent_set_key (
serpent.key, password, 256 );
Serpent_encrypt (
serpent.key, plainText, cipherText );
// plainText[16] = Serpent⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&serpent, 0,
sizeof ( SERPENT_STATIC_DATA ) );
Serpent_set_key (
serpent.key, password, 256 );
Serpent_decrypt (
serpent.key, cipherText, plainText );
// Speed ECB Cipher Functions
// Original Submission Source
Speed_set_key (
speed_ikey speedKey,
const speed_key key );
Speed_encrypt (
const speed_ikey speedKey,
const speed_data plainText,
speed_data cipherText );
Speed_decrypt (
const speed_ikey speedKey,
const speed_data cipherText,
speed_data plainText );
// cipherText[16] = Speed ( plainText[16] )
// PARAM: password[32]
memset (
&speed, 0,
sizeof ( SPEED_STATIC_DATA ) );
Speed_set_key (
speed.key, password );
Speed_encrypt (
speed.key, plainText, cipherText );
// plainText[16] = Speed⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&speed, 0,
sizeof ( SPEED_STATIC_DATA ) );
Speed_set_key (
speed.key, password );
Speed_decrypt (
speed.key, cipherText, plainText );
// Twofish ECB Cipher Functions
// Original Submission Source
Twofish_set_key (
TWOFISH_DATA *twofish,
const DWORD *key,
const DWORD keyBits );
Twofish_encrypt (
const TWOFISH_DATA *twofish,
const DWORD *plainText,
DWORD *cipherText );
Twofish_decrypt (
const TWOFISH_DATA *twofish,
const DWORD *cipherText,
DWORD *plainText );
// cipherText[16] = Twofish ( plainText[16] )
// PARAM: password[32]
memset (
&twofish, 0,
sizeof ( TWOFISH_STATIC_DATA ) );
Twofish_set_key (
&twofish.key, password, 256 );
Twofish_encrypt (
&twofish.key, plainText, cipherText );
// plainText[16] = Twofish⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&twofish, 0,
sizeof ( TWOFISH_STATIC_DATA ) );
Twofish_set_key (
&twofish.key, password, 256 );
Twofish_decrypt (
&twofish.key, cipherText, plainText );
// UnicornA ECB Cipher Functions
// Original Submission Source
Unicorn_set_key (
BYTE *unicornKey,
const BYTE *key );
Unicorn_encrypt (
const BYTE *unicornKey,
const BYTE *plainText,
BYTE *cipherText );
Unicorn_decrypt (
const BYTE *unicornKey,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = UnicornA ( plainText[16] )
// PARAM: password[32]
memset (
&unicorn, 0,
sizeof ( UNICORNA_STATIC_DATA ) );
Unicorn_set_key (
unicorn.key, password );
Unicorn_encrypt (
unicorn.key, plainText, cipherText );
// plainText[16] = UnicornA⁻¹ ( cipherText[16] )
// PARAM: password[32]
memset (
&unicorn, 0,
sizeof ( UNICORNA_STATIC_DATA ) );
Unicorn_set_key (
unicorn.key, password );
Unicorn_decrypt (
unicorn.key, cipherText, UnicornA );
Multi-Cryptography
256bit key - 128bit block - 16x CBC Ciphers
AES & NESSIE & CRYPTREC Process
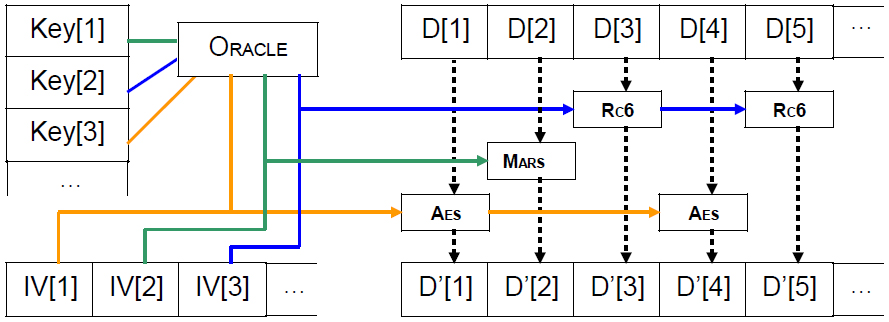
Cipher Selection
// Multi-Cryptography ECB Wrapper
typedef enum {
ANUBIS_ALG=0,
CAMELLIA_ALG,
CAST256_ALG,
CLEFIA_ALG,
FROG_ALG,
HIEROCRYPT3_ALG,
IDEANXT128_ALG,
MARS_ALG,
RC6_ALG,
RIJNDAEL_ALG,
SAFERP_ALG,
SC2000_ALG,
SERPENT_ALG,
SPEED_ALG,
TWOFISH_ALG,
UNICORNA_ALG
} ENUM_ALG;
Multi_single_setkey (
MULTI_STATIC_DATA *multiECB,
const ENUM_ALG cipher,
const BYTE *password );
Multi_ECB_single_encrypt (
const MULTI_STATIC_DATA *multiECB,
const ENUM_ALG cipher,
const BYTE *plainText,
BYTE *cipherText );
Multi_ECB_single_decrypt (
const MULTI_STATIC_DATA *multiECB,
const ENUM_ALG cipher,
const BYTE *cipherText,
BYTE *plainText );
// cipherText[16] = λ ( cipher ) ( plainText[16] )
// PARAM: password[32]
Multi_single_setkey (
&multiECB, cipher, password );
Multi_ECB_single_encrypt (
&multiECB, cipher, plainText, cipherText );
// plainText[16] = λ⁻¹ ( cipher ) ( cipherText[16] )
// PARAM: password[32]
Multi_single_setkey (
&multiECB, cipher, password );
Multi_ECB_single_decrypt (
&multiECB, cipher, cipherText, plainText );
// Multi-Cryptography CBC In-Place Wrapper
typedef enum {
OBFUNC_OK=0,
OBFUNC_OUTOFMEM,
OBFUNC_INVALID,
OBFUNC_STOP
} OBFUNC_RETV;
Multi_setkey (
MULTI_DATA *multiCBC,
const BYTE *initializationVectors,
const BYTE *password1,
const BYTE *password2,
DWORD nonce );
OBFUNC_RETV Multi_CBC_encrypt (
MULTI_DATA *multiCBC,
const DWORD length,
BYTE *buffer,
perc_callback_t progressCallback,
void *progressDescriptor,
test_callback_t stopCallback,
void *stopDescriptor );
OBFUNC_RETV Multi_CBC_decrypt (
MULTI_DATA *multiCBC,
const DWORD length,
BYTE *buffer,
perc_callback_t progressCallback,
void *progressDescriptor,
test_callback_t stopCallback,
void *stopDescriptor );
// buffer¹[length] = Multi ( buffer[length] )
// PARAM: password1[32] + password2[32]
// PARAM: initializationVectors[16*16]
// PARAM: progressCallback + progressDescriptor
// ( NULL + NULL ⇒ show no progress )
// PARAM: stopCallback + stopDescriptor
// ( NULL + NULL ⇒ no stop test )
Multi_setkey (
&multiCBC, initializationVectors,
password1, password2, nonce );
Multi_CBC_encrypt (
&multiCBC, length, buffer,
NULL, NULL, NULL, NULL );
// buffer[length] = Multi⁻¹ ( buffer¹[length] )
// PARAM: password1[32] + password2[32]
// PARAM: initializationVectors[16*16]
// PARAM: progressCallback + progressDescriptor
// ( NULL + NULL ⇒ show no progress )
// PARAM: stopCallback + stopDescriptor
// ( NULL + NULL ⇒ no stop test )
Multi_setkey (
&multiCBC, initializationVectors,
password1, password2, nonce );
Multi_CBC_decrypt (
&multiCBC, length, buffer,
NULL, NULL, NULL, NULL );
 Download Source & Redistributable DLL
 Manual EN
 SourceForge Homepage
 [C Code] CSPRNG Functions | 512bit Hashing